Best HWID Spoofer in 2026 for Fast Unbans on Fortnite, Valorant and Rust
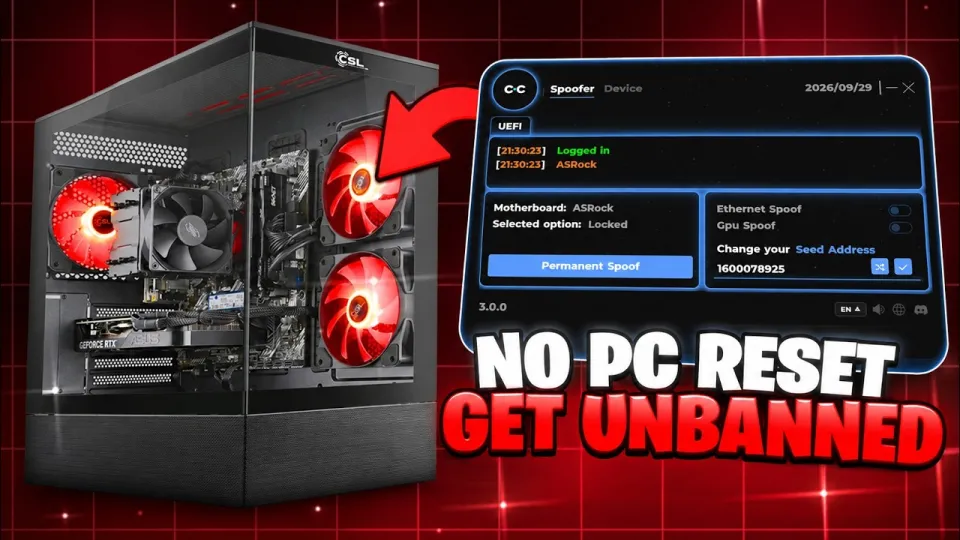
Video: The Ultimate HWID Spoofer Tutorial 2026 – Full Guide To Get Unbanned Fast
· based on the channel clixx
The best HWID spoofer in 2026 is one that changes every hardware identifier an anti-cheat reads — disk serials, SMBIOS strings, MAC addresses and volume IDs — and keeps those changes after a reboot, so a banned machine is treated as a new one. A working tool of this kind is distributed through the cethcheats.cc store, which the clixx breakdown walks through step by step, from the interface overview to the installation process. The point is not to hide a cheat but to reset the fingerprint that got your account and PC flagged in the first place.
What an HWID spoofer actually changes
An HWID ban does not target your game account; it targets the machine, which is why a fresh account on the same PC is usually banned again within minutes. Anti-cheat clients such as Easy Anti-Cheat, BattlEye and Vanguard build a hardware fingerprint from several sources at once: the volume serial number of your system drive, the disk and partition serials, SMBIOS and motherboard UUIDs, the BIOS serial, the machine GUID in the Windows registry, network adapter MAC addresses and, on some titles, monitor and peripheral identifiers. A spoofer intercepts or rewrites those values at the driver level so the collected fingerprint no longer matches the one stored in the ban database.
That distinction matters when you compare tools. A "cleaner" only deletes traces and registry keys; a real spoofer changes what the anti-cheat reads on the next launch. The strongest products combine both, and they also handle the traces left behind by previously installed cheat software, because leftover drivers are a separate detection vector.
What the clixx tutorial covers and where to get the tool
The clixx video is structured as a full walkthrough of one specific product rather than a comparison, and it moves from a general overview into features, settings and finally installation. The store behind it is cethcheats.cc, and the video description lists a 5% discount code, DENYS, for purchases there. A Discord community at discord.gg/ceth is linked for support and updates.
The chapters in the description give a clear picture of the pacing: introduction, spoofer overview, available features, configuration and settings, then the installation process. The installation segment begins around the two-minute mark, which tells you the tool is presented as a quick setup rather than a long manual procedure — most of the runtime goes to explaining options before anything is installed.
Supported games and compatibility
Compatibility is the first thing to check, because spoofing methods differ between anti-cheat vendors and a tool that works on one engine can fail on another. The games named in the video are Fortnite, Warzone, Rust, CS2, Rainbow Six Siege, Apex Legends and Valorant, with the description noting "and more." In practice that list spans Easy Anti-Cheat (Fortnite, Rust, Apex Legends), BattlEye (Rainbow Six Siege, and Warzone through its own layer) and Vanguard (Valorant), which is the hardest of the three to spoof because it runs at boot.
Before you buy anything, confirm three things: that your specific game is listed by name, that the tool supports your Windows version, and that the vendor states whether the spoof is temporary or permanent. Valorant in particular is the title people search for most ("how to fix hwid ban in valorant"), and it is also the one where sloppy tools fail most often.
Temporary versus permanent spoofing
A temporary spoof lasts until you reboot or until the tool is closed, which is enough to log in and play a session but leaves the original identifiers in place afterward. A permanent spoof writes the changes so they persist across restarts, and it is the option most banned players actually want, since a single reboot should not undo the fix.
When a vendor advertises a "perm hwid spoofer," verify how it behaves in these cases:
- After a normal Windows restart, not just a sleep or hibernate cycle.
- After a Windows update, which can rewrite driver and registry entries.
- After the anti-cheat client updates, since detection routines change with patches.
- After uninstalling the spoofer, so you know how to return the machine to stock values.
A permanent spoof that survives all four is worth the higher price; a cheap tool that resets on reboot means repeating the whole procedure every session.
Step-by-step setup, based on the tutorial's flow
The video's order — overview, features, configuration, installation — mirrors how you should approach any spoofer, because configuring before installing avoids a half-applied spoof. A sensible sequence looks like this:
- Disable antivirus real-time protection temporarily; spoofers touch drivers and are commonly flagged as false positives.
- Close the game and its launcher completely, including background anti-cheat services.
- Create a system restore point, so a failed spoof does not leave you reinstalling Windows.
- Open the tool, review the configuration options, and select what to spoof — disk, SMBIOS, MAC and registry entries are usually separate toggles.
- Run the spoof, wait for confirmation, then reboot if the tool requires it.
- Verify the new values with a hardware info utility before launching the game.
The configuration screen is where most failures happen: leaving one identifier unchecked can be enough for the anti-cheat to re-link the machine to the old ban. If the tool offers a preset for your specific game, use it rather than toggling items manually.
What to check before paying for any spoofer
Price and interface matter far less than whether the tool is maintained, because anti-cheat updates break spoofing methods regularly. Look for a changelog with recent entries, a support channel where the developer responds, and clear documentation of which Windows builds are supported. A Discord server, like the one linked alongside the store in this video, is usually the fastest way to judge whether a product is alive or abandoned.
Also treat any spoofer as a security decision: it installs a kernel-level driver, so it has the same access as the anti-cheat it is trying to evade. Buy from a vendor with a public storefront and a refund policy, scan the installer, and avoid anything distributed as a random archive from a file host. Finally, remember that spoofing only resets the hardware fingerprint — it does not unban the account, and it does not make cheating undetectable on the new one.
Conclusion
An HWID spoofer is a hardware fingerprint reset, and the best one in 2026 is the tool that covers every identifier, survives reboots and updates, and names your game explicitly. The clixx breakdown is useful precisely because it shows the interface and the configuration options before installation, which is where most buyers want to look first. If you want to test the product shown in that walkthrough, you can get the spoofer at cethcheats.cc and apply the DENYS code for 5% off. Whichever tool you choose, verify the permanent mode, keep a restore point, and confirm the new IDs before you launch the game again.
Key takeaways
- An HWID spoofer replaces the hardware identifiers a game's anti-cheat reads, so a banned machine looks like a new one.
- The breakdown by clixx covers a spoofer sold through cethcheats.cc, with a 5% discount code DENYS.
- Supported titles listed include Fortnite, Warzone, Rust, CS2, Rainbow Six Siege, Apex Legends and Valorant.
- Setup in the video is split into overview, features, configuration and installation, with installation starting around the two-minute mark.
- Spoofers are temporary by default; a permanent option must survive reboots and is the main thing to verify before buying.
Questions & answers
Does an HWID spoofer actually get you unbanned?
It does not lift the ban on your account, but it changes the hardware identifiers the anti-cheat reads, so a new account on the same PC is no longer matched to the banned machine. That is why spoofing is usually paired with a fresh account and a clean game install.
Is a free HWID spoofer safe to use?
Free spoofers are the most common source of malware in this space, because they require kernel-level access to your system. If you use one, run it in a virtual machine first and scan the installer, but a paid tool with a public storefront and active support is the lower-risk option.
How long does a permanent HWID spoof last?
A properly implemented permanent spoof persists across reboots and usually through Windows updates, until you deliberately revert it or the anti-cheat changes its detection method. Temporary spoofs reset as soon as you restart the PC or close the tool.
Which games can an HWID spoofer cover?
Coverage depends on the anti-cheat: Easy Anti-Cheat titles like Fortnite, Rust and Apex Legends are the most commonly supported, BattlEye titles such as Rainbow Six Siege next, and Vanguard-protected Valorant is the hardest because it loads at boot. Always confirm your specific game is listed before buying.
Source: The Ultimate HWID Spoofer Tutorial 2026 – Full Guide To Get Unbanned Fast · Markdown version